Dropzone
Autonomous AI investigates security alerts, enhancing SOC efficiency.
Key Takeaways
- What it is
- Autonomous AI investigates security alerts, enhancing SOC efficiency.
- Pricing
- $500 per month
- Best for
- Autonomous Alert Investigations
- Integration with Existing Tools
- Pre-trained AI Agents
- Rating
- 4.6/5
What is Dropzone?
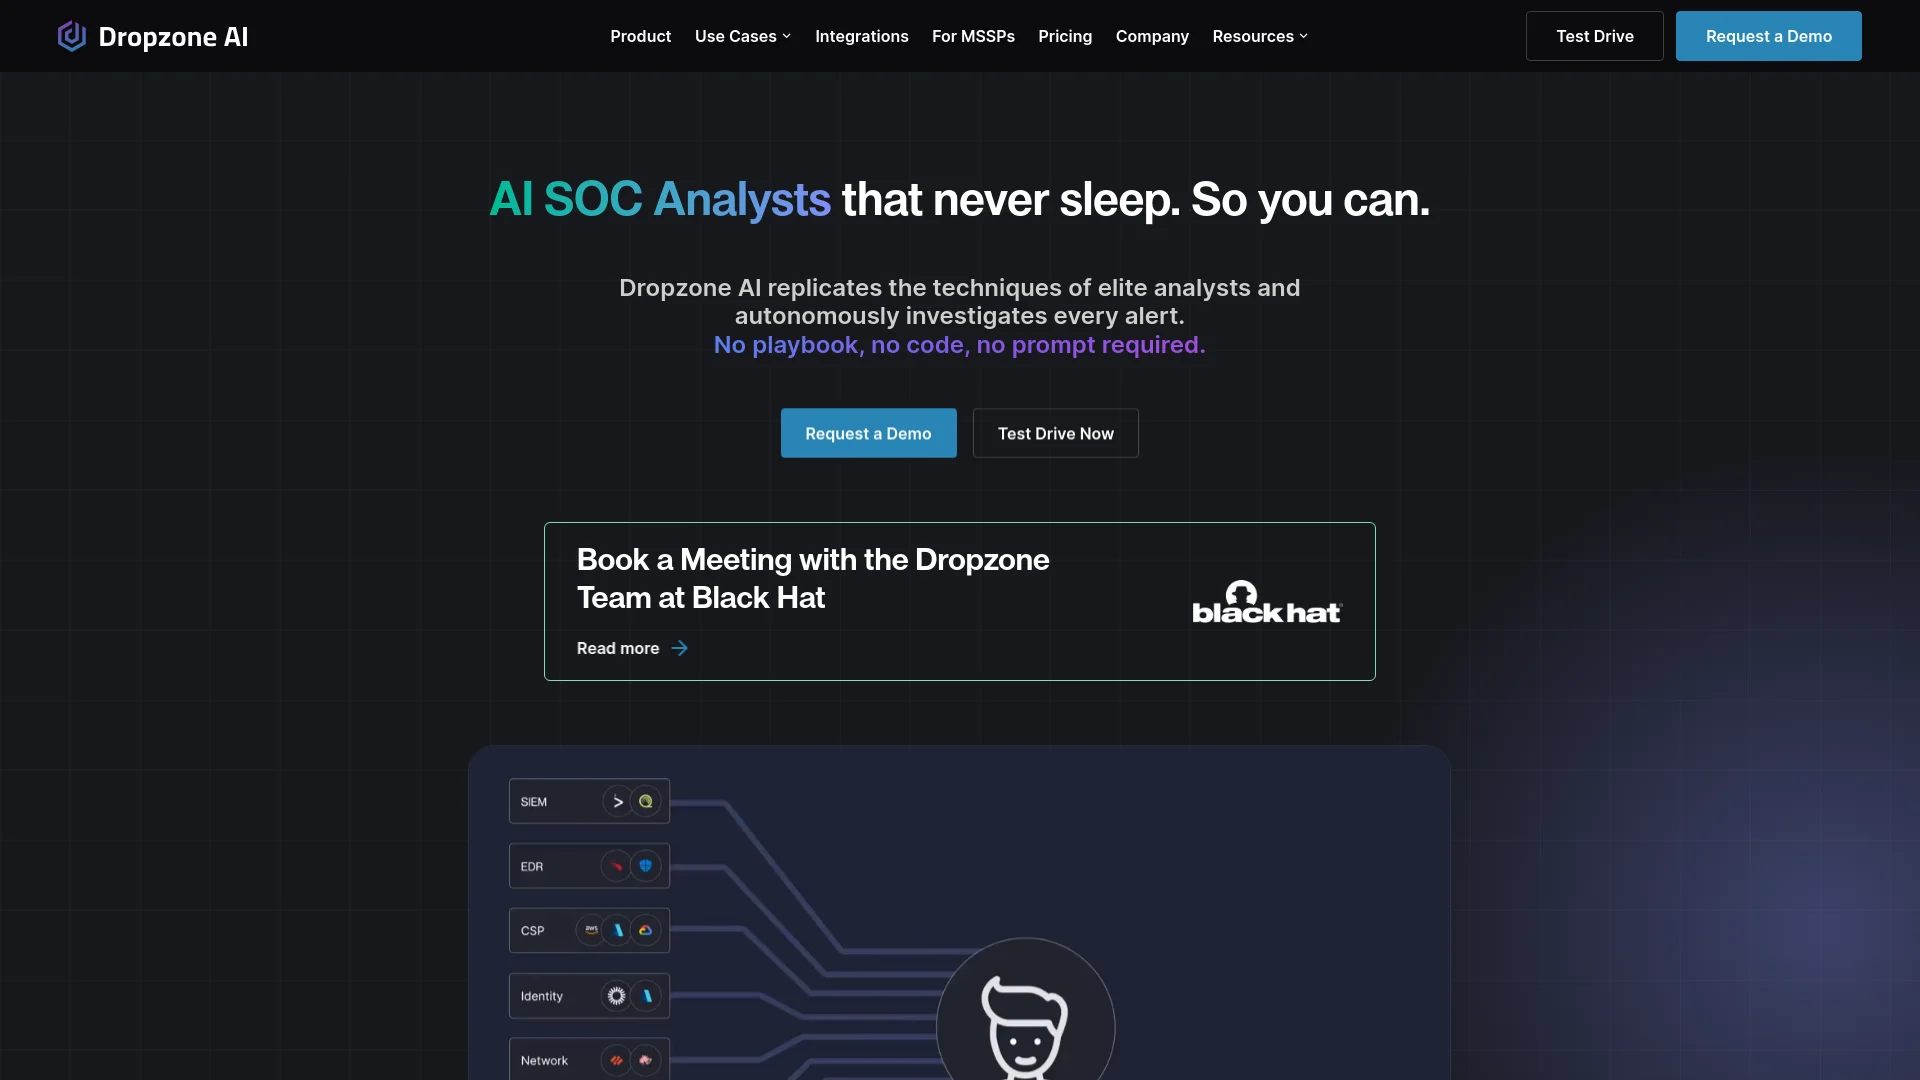
Dropzone is an advanced AI tool designed to enhance the efficiency of Security Operations Centers (SOCs) by automating the investigation of security alerts. This tool uses sophisticated AI technology to handle alerts autonomously, freeing up cybersecurity teams to focus on more complex tasks. Dropzone operates without the need for playbooks, code, or prompts, making it a powerful asset in the fight against cybersecurity threats.
Dropzone's distinctive feature is its autonomous, pre-trained AI agents that do not require playbooks, offering immediate efficiency. Its comprehensive integration with existing cybersecurity tools and evidence-based reporting system further distinguishes it in the cybersecurity field.
Dropzone enhances SOC operations by autonomously handling security alerts and integrating seamlessly with existing systems. Its ability to reduce response times and focus on real threats makes it an essential tool for modern cybersecurity. With its robust AI technology and user-centric features, Dropzone optimizes security processes and empowers teams to address more strategic challenges.
Who is Using Dropzone?
Corporate Security Teams
Manages high volumes of security alerts efficiently.
Managed Security Service Providers (MSSPs)
Enhances service offerings by integrating Dropzone into their operations.
Financial Institutions
Protects sensitive data and meets regulatory requirements through automated investigations.
Healthcare Providers
Safeguards patient data by quickly identifying and addressing potential threats.
Uncommon Use Cases
Non-profits protect donor information; educational institutions prevent data breaches cost-effectively.
Key Features
Rating Breakdown
Pricing Plans
Standard Plan
$500 per month
- Providing full alert investigation capabilities and standard integration options
Enterprise Plan
- Custom pricing based on organizational needs
- Including advanced features and dedicated support
Which Dropzone plan should you pick?
Start with the standard AI SOC Analyst subscription for core investigations, choose Enterprise for a dedicated environment and custom workflows, or choose MSSP for multi-tenant customer operations.
Enterprise Plan
Good for enterprise teams that need a dedicated single-tenant environment, custom workflows, and premium support.
MSSP
Good for managed security providers that need a dedicated multi-tenant environment and pooled AI analyst capacity.
Dropzone Use Cases
Phishing investigation
Analyze email headers, links, attachments, sender behavior, and downstream impact across connected security systems.
Outcome: Generate a report and optionally quarantine messages, disable accounts, or escalate threats.
Identity alert investigation
Correlate login patterns, access anomalies, privilege escalations, IAM data, and SSO application logs.
Outcome: Produce faster, more detailed identity-alert investigations.
Cloud security alert investigation
Pull relevant evidence from cloud providers and connected security tools to investigate cloud alerts.
Outcome: Prioritize real cloud threats while reducing manual triage.
Endpoint investigation
Investigate endpoint detections using EDR telemetry and related identity, network, and threat-intelligence context.
Outcome: Deliver evidence-backed conclusions for endpoint alerts.
Threat hunting and contextual inquiry
Use the chatbot to query integrated tools and data sources with natural-language questions.
Outcome: Accelerate tactical lookups and enrichment.
Workflow Ideas with Dropzone
Automated phishing response
- 1Ingest a phishing alert from an email security tool or SIEM
- 2Analyze headers, URLs, attachments, sender behavior, and blast radius
- 3Trigger containment actions such as quarantine, account disablement, or escalation
Investigation review and tuning
- 1Open completed investigations in the review queue
- 2Validate conclusions, evidence, and reasoning against internal procedures
- 3Capture feedback through Context Memory or Custom Strategies
Automated remediation workflow
- 1Select an investigation or system event trigger
- 2Write a sandboxed Python Response Action
- 3Review execution status, output, errors, and audit logs
How Dropzone fits into your stack
Broad Tool Compatibility
Integrates seamlessly with essential cybersecurity tools and platforms.
Data Enrichment
Connects with data sources like VirusTotal and UrlScan.io for enhanced alert analysis.
Custom API Access
Provides APIs for tailored integrations based on organizational needs.
Continuous Updates
Regularly updated to ensure compatibility with new tools and technologies.
Pros
- +Increased Efficiency: Automates the triage, investigation, and response processes, reducing Mean Time to Respond (MTTR).
- +Focus on Real Threats: Allows analysts to concentrate on more sophisticated threats by managing routine investigations.
- +Scalability: Capable of handling 100% of alerts, ensuring comprehensive threat coverage.
- +Enhanced Accuracy: Continuously refines its analyses for improved precision over time.
Cons
- −Complexity in Initial Setup: May require significant effort to integrate with existing infrastructure.
- −Dependence on Data Quality: The effectiveness of the tool depends on the quality and availability of data from integrated systems.
- −Potential Overreliance: Risks of excessive dependence on automation, potentially undervaluing human intuition and oversight.
Limitations & when to consider alternatives
Known limitations
- Investigation capacity is metered. The standard subscription includes up to 4,000 full investigations per year per AI analyst; additional capacity may require purchase.
- Connector deployment requires Linux and Docker. The private connector requires Docker Engine, an x86_64 Linux container host, at least 1 GB memory, disk, and one CPU core.
- Chat is not a full investigation. The chatbot is intended for tactical lookups and enrichment rather than complete investigations.
- Custom investigation questions have a limit. Up to 10 additional questions can be added per investigation, processed in batches of five.
- Notes do not directly change AI behavior. Investigation notes provide collaboration space but currently do not influence AI behavior directly.
Look elsewhere when
- You need a native mobile app.
- You need publicly posted self-service pricing.
- Your primary requirement is image understanding.
- You need customer-data fine-tuning.
How to Use Dropzone
- 1
Connect security tools
Configure alert sources, data sources, connectors, and API keys under Settings > Integrations.
- 2
Review investigations
Open completed investigations, inspect findings and evidence, and approve or modify conclusions.
- 3
Use analyst chat
Ask natural-language questions against integrated data for tactical lookups and enrichment.
- 4
Add organizational context
Create Context Memory items for facts, exceptions, and environment-specific knowledge.
- 5
Customize investigation behavior
Create Custom Strategies with organization-specific logic, priorities, guidance, and investigation questions.
- 6
Automate response actions
Configure triggers and sandboxed Python actions to notify systems, enrich records, or perform remediation.
Who is Dropzone For?
Security operations teams
Dropzone automates repetitive Tier 1 alert investigation so SOC analysts can focus on higher-value security work.
Enterprise security teams
Enterprise deployments provide a dedicated single-tenant environment, custom workflows, and premium support.
MSSPs and MDRs
MSSPs can use a dedicated multi-tenant environment and pool AI analysts across customer environments.
Junior SOC analysts
The COACH extension previews the investigation workflow and helps junior analysts learn investigation techniques.
Security leaders
Dashboards, investigation metrics, audit trails, and role-based access support operational oversight.
Frequently Asked Questions
What does Dropzone AI investigate?
Dropzone autonomously investigates security alerts across phishing, network, identity, cloud, endpoint, and insider-threat workflows.
What integrations does Dropzone AI support?
It supports more than 90 integrations across SIEM, EDR, cloud, identity, email, network, SOAR, and threat-intelligence categories.
Does Dropzone AI support SSO?
Yes. Supported login options include Google, Microsoft, and custom SAML identity providers.
Does Dropzone AI train models on customer data?
No. Dropzone states that customer data is not used to train Dropzone or subprocessors' models.
Can Dropzone AI automate remediation?
Yes. Response Actions can trigger notifications, remediation workflows, ticket enrichment, and policy-driven actions.
How is pricing calculated?
Pricing is based on investigation capacity, with up to 4,000 full investigations per year per AI analyst and additional capacity available.
Community reviews
Be the first to share your experience.
Sign in to leave a review for Dropzone.
Dropzone Alternatives
Looking for alternatives to Dropzone? Here are similar tools in the same category:
Learn to Master Dropzone
With Skill Leap courses
Get in-depth training on Dropzone and 50+ other AI tools with our expert-led video courses.
Start 7-Day Free Trial